GDPR Checklist for Clinics: Choosing EU Practice Software

In today's digital age, protecting sensitive patient data is a top priority for clinics and healthcare facilities in the European Union. The General Data Protection Regulation (GDPR) has established strict requirements for how healthcare organizations collect, process, and store personal data. In this comprehensive guide, we'll examine the key aspects of GDPR compliance for clinics, the obligations of healthcare providers, and how Electronic Health Record (EHR) systems like CloudMedico can help achieve and maintain compliance.
What is GDPR and Why It Matters for Clinics
The General Data Protection Regulation (GDPR) is an EU legislative framework that came into effect on May 25, 2018. It establishes strict rules for protecting the personal data of EU citizens and imposes significant obligations on organizations that process such data.
For clinics and healthcare facilities, GDPR is particularly important because they process special categories of personal data - specifically, health data - which is considered extremely sensitive and requires additional levels of protection. Health data includes any information about an individual's physical or mental health, including medical records, diagnoses, treatments, and medical history.
Non-compliance with GDPR can lead to significant penalties, including fines of up to €20 million or 4% of global annual turnover, whichever is higher. Beyond the financial implications, a data breach can seriously damage a clinic's reputation and undermine patient trust.
Key Obligations for Clinics Under GDPR
Legal Basis for Processing Medical Data
Under GDPR, clinics must have a legal basis for processing health data. For healthcare providers, the most common legal bases are:
- Contractual necessity - for providing healthcare services to patients
- Legal obligation - for maintaining medical records as required by law
- Vital interests - when processing is necessary to protect someone's life
- Public interest - for public health reasons
- Consent - where specifically required and requested
Patient Consent
Although consent is not always necessary for processing health data, in certain cases clinics must obtain explicit consent from patients. Consent must be:
- Freely given - without pressure or coercion
- Specific - for particular processing purposes
- Informed - with clear information about how data will be used
- Unambiguous - through positive action, not pre-selected
- Withdrawable - patients must be able to withdraw consent at any time
Transparency and Privacy Policies
Clinics must be transparent about how they collect, process, and store patient data. This includes providing clear and understandable privacy policies that explain:
- What data is collected and why
- How the data is used
- Who the data is shared with (if anyone)
- How long data is retained
- Patients' rights regarding their data
- How patients can exercise these rights
Appointing a Data Protection Officer (DPO)
Healthcare organizations that process large amounts of health data are often required to appoint a Data Protection Officer (DPO). The DPO is responsible for monitoring compliance with GDPR, providing advice on data protection obligations, and serving as a contact point for supervisory authorities.
Data Protection Impact Assessment (DPIA)
Clinics must conduct Data Protection Impact Assessments (DPIAs) when data processing is likely to result in a high risk to individuals' rights and freedoms. Given the sensitive nature of health data, DPIAs are often necessary for clinics, particularly when implementing new technologies or systems.
Patient Rights Under GDPR
GDPR provides patients with various rights regarding their personal data. Clinics must ensure they can effectively respond to patients' requests to exercise these rights:
Right of Access
Patients have the right to request a copy of their personal data held by the clinic. Clinics must provide this information in an accessible format within one month of the request.
Right to Rectification
Patients have the right to request correction of inaccurate or incomplete personal data. This is particularly important in healthcare, where accurate information is vital for safe and effective treatment.
Right to Erasure
Also known as the "right to be forgotten," patients can request the deletion of their personal data under certain conditions. However, this right is not absolute and may be limited when data is necessary for legal reasons, such as maintaining medical records for the period required by law.
Right to Data Portability
Patients have the right to receive their personal data in a structured, commonly used, and machine-readable format and to transfer it to another healthcare provider. This facilitates continuity of care when patients change providers.
Practical Tips for Managing Patient Requests
- Establish clear procedures for handling patient rights requests
- Train staff to recognize and forward such requests
- Document all requests and responses
- Verify the identity of the requester before disclosing any personal data
- Respond within the required timeframes (typically one month)
Technical and Organizational Measures for GDPR Compliance
GDPR requires clinics to implement appropriate technical and organizational measures to protect patient data. These measures should be proportionate to the risks and take into account the state of the art, the costs of implementation, and the nature, scope, context, and purposes of processing.
Data Encryption
Encryption is a key security measure for protecting sensitive health data. Clinics should implement encryption for data both in transit (e.g., when sent over the internet) and at rest (e.g., on servers or databases).
Access Control
Clinics must implement strict access controls to ensure that only authorized personnel have access to patient data and only to the extent necessary to perform their duties. This includes:
- Unique user identifiers for each staff member
- Strong password policies
- Multi-factor authentication
- Role-based privilege management
- Regular review of access rights
Audit Logging
Maintaining detailed audit logs is essential for monitoring access and changes to patient data. Audit logs should record who accessed what data, when, and for what purpose. This not only helps detect unauthorized access but also demonstrates compliance with GDPR.
Backups
Regular backups are essential for ensuring the availability and resilience of processing systems and services. Backups should be encrypted and securely stored, with regular testing to ensure they can be effectively restored in case of an incident.
Data Breach Procedures
Clinics must have clear procedures for detecting, reporting, and investigating data breaches. Under GDPR, breaches that are likely to risk the rights and freedoms of individuals must be reported to the relevant supervisory authority within 72 hours of becoming aware of them. In some cases, affected individuals must also be notified.
How Electronic Health Record (EHR) Systems Help with GDPR Compliance
Modern Electronic Health Record (EHR) systems can play a crucial role in helping clinics achieve and maintain GDPR compliance. By providing built-in security features and data management tools, EHR systems can simplify many aspects of GDPR compliance.
Automating Compliance Processes
EHR systems can automate many processes related to GDPR compliance, such as obtaining and recording patient consent, managing data retention periods, and generating compliance reports. This reduces administrative burden and minimizes the risk of human error.
Secure Data Storage and Management
EHR systems provide secure storage for sensitive patient data, with built-in security measures such as encryption, access control, and audit logging. This helps clinics comply with GDPR's requirement to implement appropriate technical and organizational measures to protect data.
Facilitating Patient Rights
Modern EHR systems make it easier to respond to patient requests to exercise their rights under GDPR. For example, they can allow for easy export of patient data in a portable format, implementation of corrections to inaccurate data, and management of consents.
CloudMedico: Practice Software That Helps You Apply GDPR
CloudMedico helps you apply GDPR and protect your patients' data. Key features include:
- Encryption: patient details are encrypted at rest with Google Cloud KMS, and all traffic uses HTTPS
- EU-based servers: practice and patient data is stored on our servers in Frankfurt, Germany
- Granular access controls allowing precise management of who can access what data
- An audit log that records who opened, changed or exported patient records
- Consent forms that patients sign online, with the signed copy kept in their record
- Data export: export patient details to an Excel file
- Regular security updates to address emerging threats and vulnerabilities
GDPR Compliance Checklist for Clinics
Use this checklist to assess your clinic's GDPR compliance status and identify areas that may need attention:
- Have you identified all personal data you process and documented the legal basis for processing?
- Do you have clear and transparent privacy policies that are easily accessible to patients?
- Have you implemented appropriate technical and organizational security measures?
- Do you have procedures in place for obtaining and recording patient consent where required?
- Can you effectively respond to patients exercising their rights (access, rectification, erasure, etc.)?
- Have you conducted Data Protection Impact Assessments for high-risk processing activities?
- Do you have a data breach response plan in place?
- Have you appointed a Data Protection Officer if required?
- Are your staff trained on GDPR requirements and data protection best practices?
- Do you have appropriate data processing agreements with all third-party service providers?
Frequently Asked Questions
Do all clinics need to appoint a Data Protection Officer?
Not all clinics are required to appoint a DPO. Under GDPR, you must appoint a DPO if: (1) you are a public authority; (2) your core activities require regular and systematic monitoring of individuals on a large scale; or (3) your core activities consist of large-scale processing of special categories of data, including health data. Many healthcare providers fall into the third category, but small practices with limited patient numbers may not need a dedicated DPO.
How long can we keep patient data?
GDPR requires that personal data be kept for no longer than necessary for the purposes for which it was collected. However, for medical records, there are often legal requirements that specify minimum retention periods. These legal obligations take precedence, and you can retain medical records for as long as required by applicable healthcare laws. It's important to have a clear data retention policy that balances GDPR principles with legal requirements for medical records.
Can we share patient data with other healthcare providers?
Yes, you can share patient data with other healthcare providers when necessary for the provision of healthcare. This is typically covered under the legal bases of vital interests, public interest in the area of public health, or for the provision of health or social care. However, you should ensure that patients are informed about such sharing in your privacy policy, and that appropriate security measures are in place for the transfer of data.
What should we do in case of a data breach?
In case of a data breach, you should immediately activate your data breach response plan. This typically involves: (1) containing the breach to prevent further data loss; (2) assessing the nature and scope of the breach and the risks to affected individuals; (3) notifying the relevant supervisory authority within 72 hours if the breach is likely to result in a risk to individuals' rights and freedoms; (4) notifying affected individuals without undue delay if the breach is likely to result in a high risk to their rights and freedoms; and (5) documenting the breach and your response to it.
Conclusion
GDPR compliance is not just a legal obligation for clinics in the EU—it's an opportunity to strengthen patient trust by demonstrating your commitment to protecting their sensitive health data. By implementing appropriate technical and organizational measures, respecting patient rights, and leveraging modern EHR systems like CloudMedico, clinics can achieve and maintain GDPR compliance while improving their overall data protection posture.
Remember that GDPR compliance is an ongoing process, not a one-time effort. Regular reviews, updates to policies and procedures, and staff training are essential to ensure continued compliance as your clinic evolves and as data protection regulations and best practices develop.
By taking a proactive approach to GDPR compliance, clinics can not only avoid potential penalties but also build stronger relationships with patients based on transparency, respect for privacy, and secure handling of sensitive health information.
Trusted by healthcare professionals all over the world
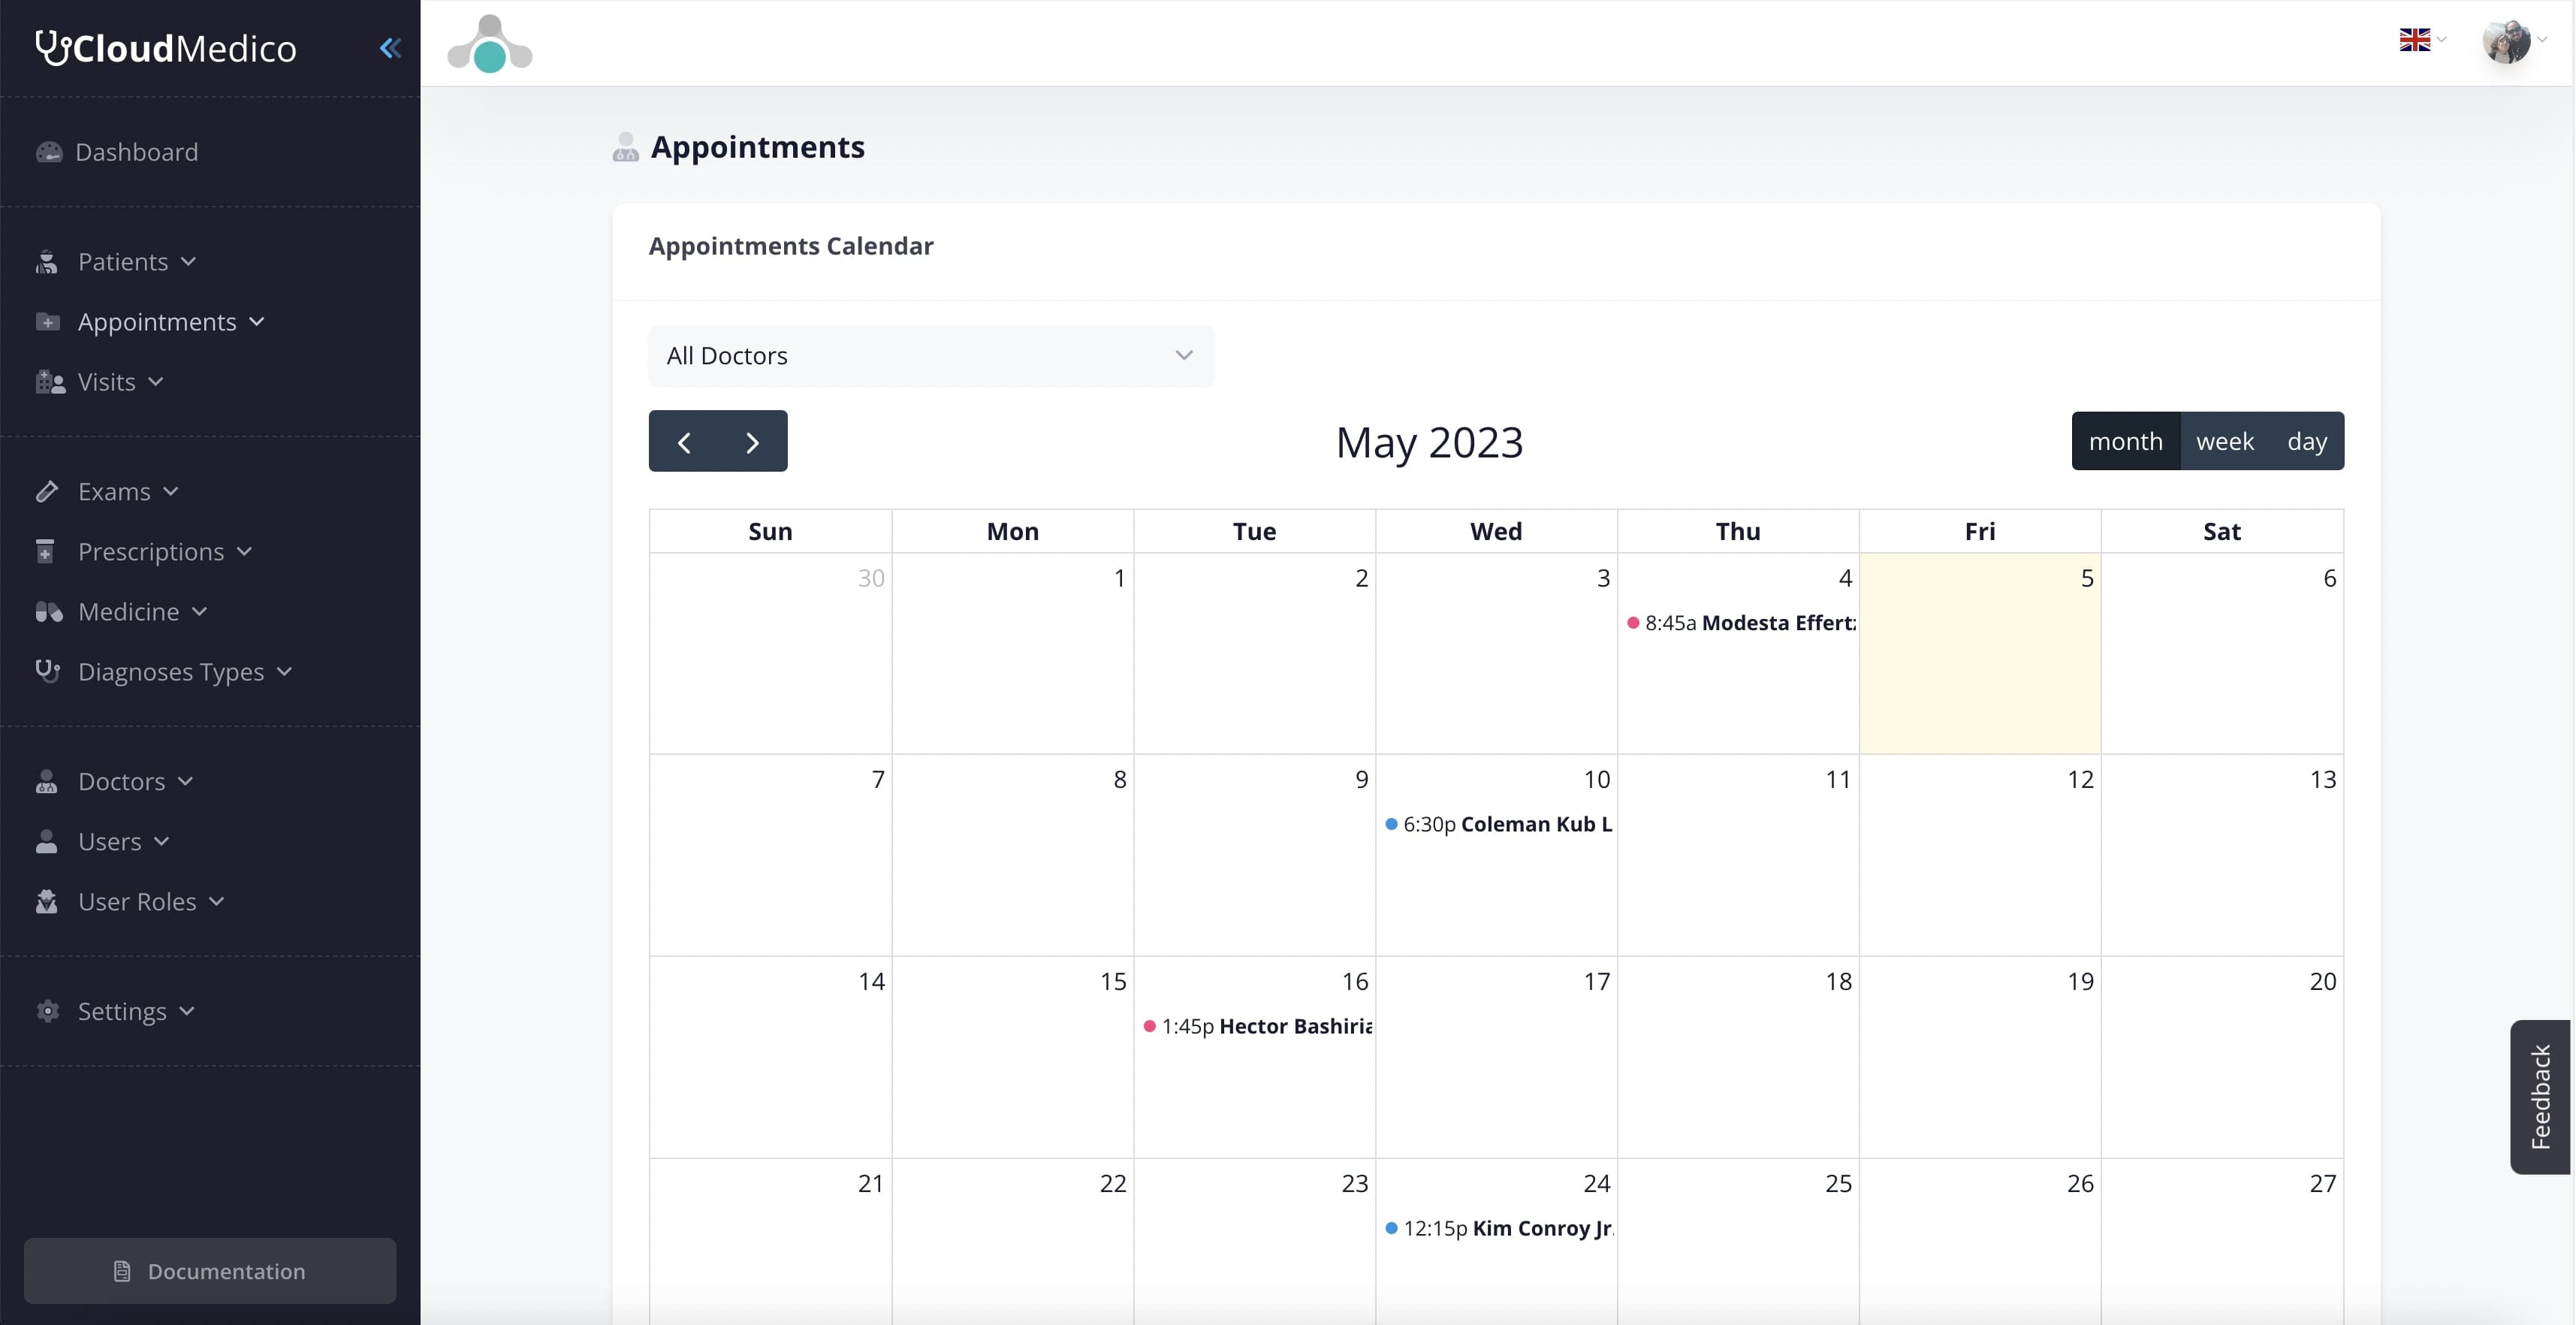
Easy Appointments Management
Latest from our Blog
Read all our latest news and takes on some industry topics.
Securely Connect ChatGPT and Claude to Your EHR with CloudMedico