GDPR & Data Protection
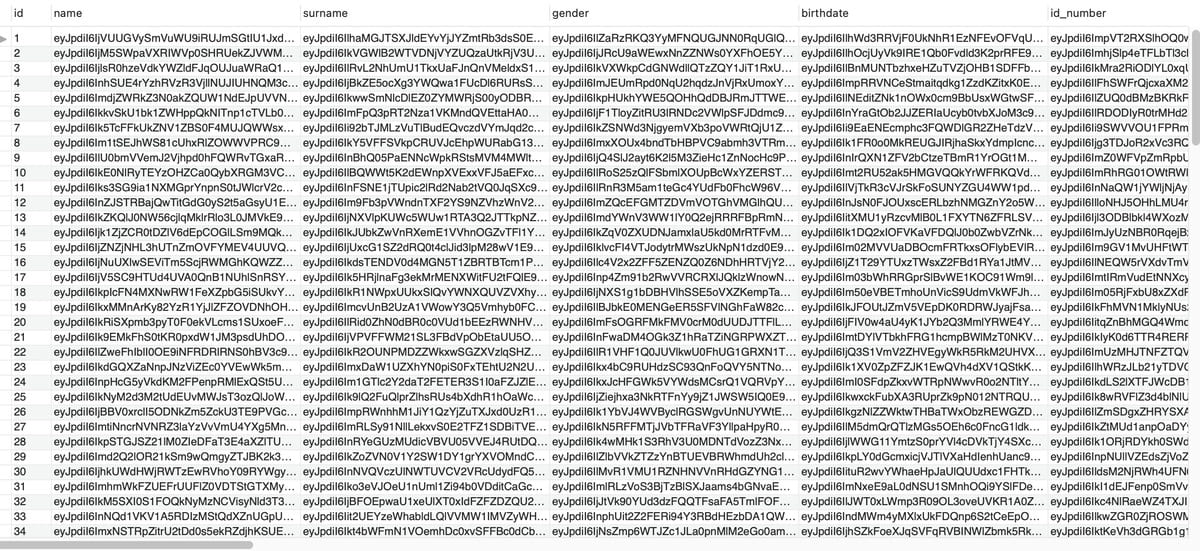
At CloudMedico, we understand that the security, privacy, and regulatory compliance of patient data is paramount. Our platform is built with GDPR compliance and data protection at its core, ensuring that all sensitive information is protected using state-of-the-art security measures.
We implement comprehensive GDPR requirements through:
- Patient details encrypted at rest with Google Cloud KMS, and all traffic over HTTPS
- Dedicated, isolated databases for each medical practice
- Application and database servers in Frankfurt, Germany (EU)
- Audit log of who viewed, changed or exported records, and of sign-ins
- Strict access controls with detailed activity tracking
- Automated twice-daily backups to encrypted storage (Google Drive)
- No selling of data, and no sharing of data for anyone else's purposes
- Full data export capabilities
As a healthcare software provider, we act solely as a data processor, providing the technical infrastructure for medical practices to securely store and manage their patient data. Each practice maintains full control over their data, with the ability to create, update, delete, or export their records at any time.
Data protection at CloudMedico is overseen by our Data Protection Officer (DPO), George Botsaris ([email protected]), and we review these measures as CloudMedico changes.
With CloudMedico, you can have peace of mind knowing that your patients' data is not only secure but also managed in full compliance with GDPR requirements, allowing you to focus on providing the best possible care.